Can your hardware wallet be tampered with? What the Ledger implant case teaches
In October 2026, Ledger confirmed that a customer's hardware wallet, bought through a third-party reseller, contained an unauthorized hardware implant. Nobody broke the secure chip. Someone modified the device around it before it reached its owner. Here's what that attack needed, a five-point check you can apply to any wallet, and how a Cryptnox card answers each point.
What happened
On 9 October 2026, Ledger said it was investigating reports of stolen funds linked to devices sold by CryptoBilis, a reseller in Southeast Asia. Two days later it confirmed that one affected wallet contained an unauthorized hardware implant added before the buyer received it.
On-chain investigators have estimated suspected losses at between $64 million and $93 million across several hundred wallets. Those figures have not been independently verified. Ledger has not confirmed a total, and says it has no indication that its own systems or its direct sales network were compromised. The reseller has stopped selling hardware wallets.
If you bought a device from that reseller, follow Ledger's advice: don't set it up. If you already use one, move your funds to a new device with a new recovery phrase.
What the attack needed
Reports describe the implant capturing what the device displays, including the 24-word recovery phrase shown during setup. With those words the attacker never needs the device again. They wait for funds to arrive and empty the wallet from anywhere.
Ledger's authenticity check (“Genuine Check”) didn't catch it, and that isn't because the check failed. It proves the secure element, the protected chip that stores the keys, is genuine. It isn't designed to inspect the rest of the device: the circuit board, the screen, the buttons, the USB or Bluetooth link. The chip was real. The implant sat next to it.
The attack needed three things:
- Room inside the device to hide an extra component.
- A secret that leaves the chip: the recovery phrase on the screen.
- Parts the authenticity check doesn't cover.
A five-point check for any hardware wallet
Ask these five questions before trusting any wallet, wherever you bought it:
| Question | Why it matters | Cryptnox card wallet |
|---|---|---|
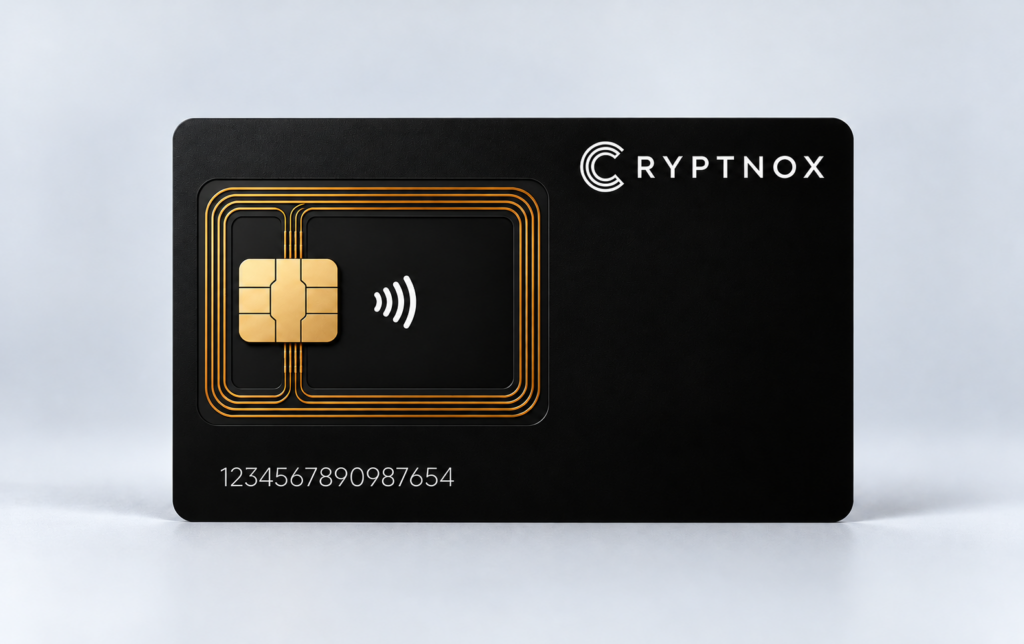
| 1. Is the device just the secure chip, or a chip plus a circuit board? | Every extra component is somewhere to hide an implant. | One EAL6+ certified secure element and an NFC antenna, laminated into a 0.76 mm card. No board, battery, port or screen. |
| 2. Is your seed ever shown, typed or printed? | A secret that leaves the chip can be copied on its way out. | No, in the default setup. The seed is generated inside the chip and never displayed. |
| 3. Does the authenticity check cover the whole device? | A check that covers only the chip leaves the rest unverified. | Yes, in practice. Every card is cryptographically signed and the Cryptnox app verifies it, and the card is essentially just the chip. |
| 4. Does the device arrive blank? | A wallet set up by someone else may use keys they know. | Yes. Cards leave the factory uninitialized, and the app detects a card that already holds a wallet. |
| 5. Where does the app come from? | A fake app can show you anything, including “genuine”. | Install the Cryptnox app only from the App Store or Google Play, never from a link or QR code inside a package. |
Why a card wallet gives a supply-chain attacker so little to work with
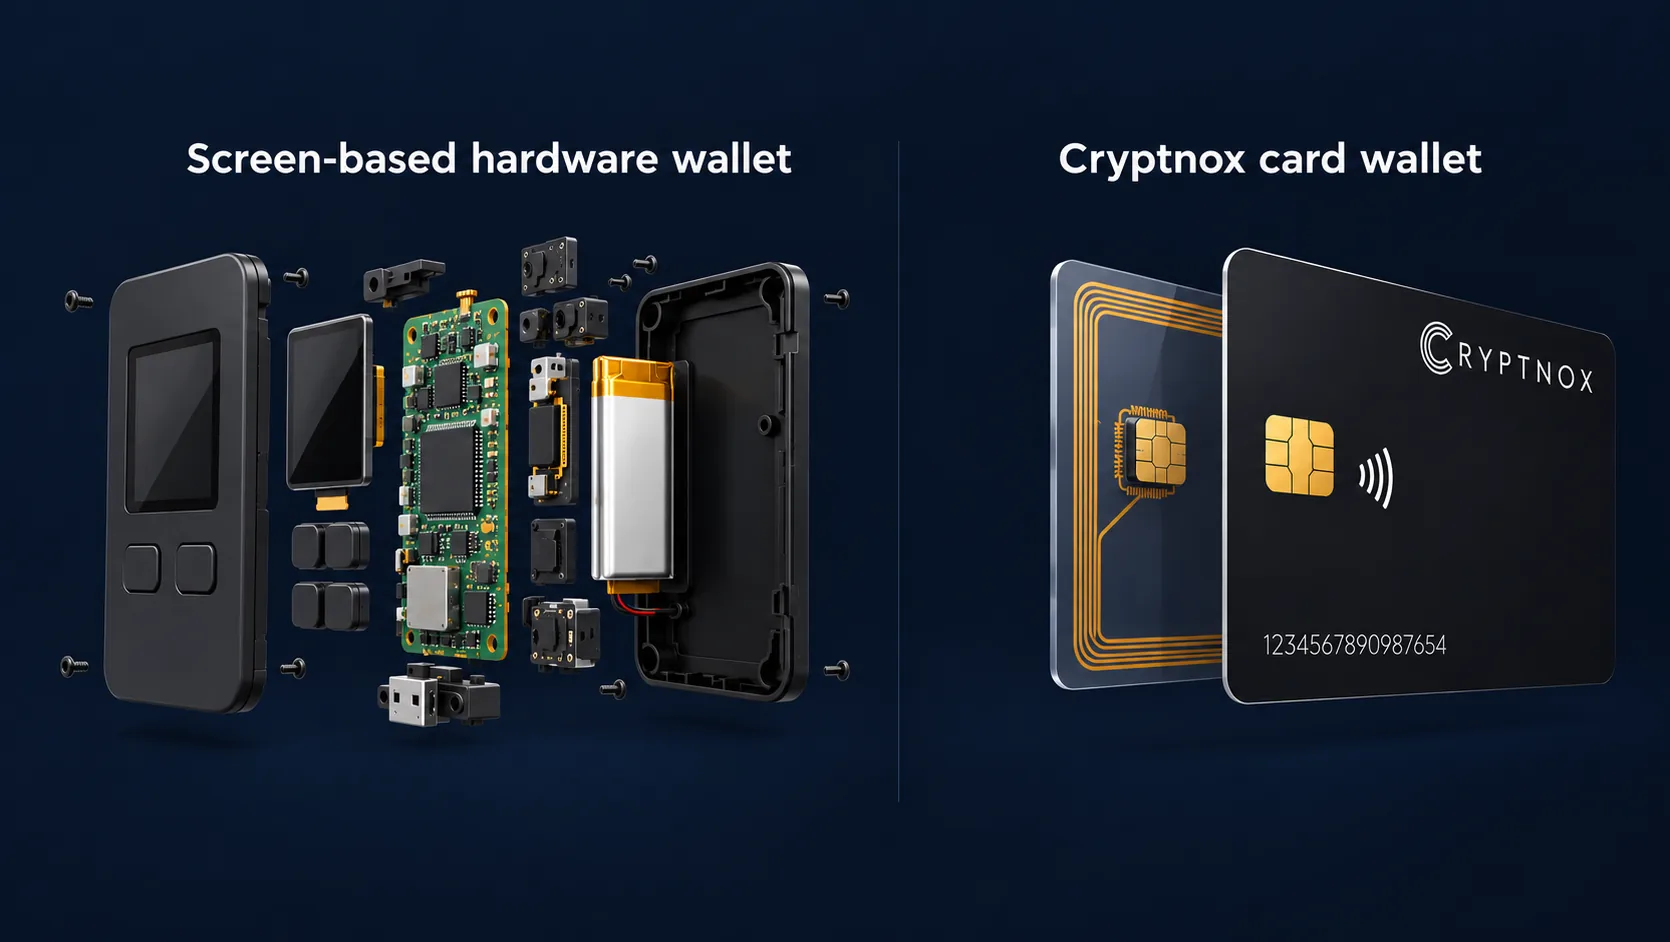
Nowhere to hide an implant. A Cryptnox wallet is a credit-card-sized NFC smart card: a chip and an antenna sealed in PVC. Adding a component means taking the card apart, and that shows. The card has no battery either. It only receives power from your phone during the second or two of a tap.
No seed to read. The Dual-Card Set ships blank. During setup, the seed is generated by the certified random number generator inside the secure elements and written to both cards. Your second card is your backup, so there are no recovery words to display, type, photograph or steal. An implant placed next to the chip would only see transactions going in and signatures coming out, and both end up public on the blockchain anyway.
The authenticity check covers what matters. Because the card is essentially just the secure element, the app's cryptographic genuineness check covers nearly the whole device. A counterfeit card loaded with keys the attacker knows can't pass it.
What a card can't protect you from
A card protects your keys. It can't protect you from being tricked, and we'd rather tell you that plainly.
If a card arrives already set up, or comes with a PIN, code or recovery words printed on paper, it's a scam, wherever you bought it. Contact us before doing anything with it.
- Your phone is the display. A card has no screen, so you review transactions in the app. Keep your phone and the app up to date, and check the receiving address before you approve. Our guide on checking a crypto wallet address before you send shows how.
- Importing a recovery phrase is optional, and it changes the model. Advanced users can import an existing 12- or 24-word phrase. If you do, the phrase passes through your phone. For the strongest protection against tampering, use the default dual-card setup with no phrase.
- Keep the backup card separate. It holds the same keys as your main card. Store it somewhere safe, apart from the card you carry.
What sets Cryptnox apart among card wallets
- Made in Switzerland. Cryptnox cards are made in Switzerland.
- Two cards, no words. The backup is a second card holding the same keys, not a sheet of paper.
- One card for crypto and secure logins. The Dual-Card Set also works as a FIDO2 security key for two-factor login to supported accounts.
- Built for developers too. Cryptnox publishes Arduino and C++ SDKs for building the card into your own projects.
- 20-year warranty on the wallet cards.
For a wider view of wallet types, see our hardware wallet comparison.
Protect your crypto with Cryptnox
Two Swiss-made cards, keys generated on the chip, no recovery words to steal.
FAQ
Was Ledger hacked?
Ledger says its own systems and direct sales were not compromised. The confirmed case involved a device modified with a hardware implant before it reached the buyer, sold through a third-party reseller.
Can a Cryptnox card be tampered with in the same way?
That attack hid a component next to the secure element and read the recovery phrase from the screen. A Cryptnox card has no circuit board or screen, and in the default setup no recovery phrase exists. Every card is cryptographically signed and verified by the app, so a counterfeit card can't pass.
Is a card wallet a good Ledger alternative?
If your main concern is physical or supply-chain tampering, a single-chip card wallet gives an attacker far less to work with. If you want a dedicated screen on the device to confirm transactions, a screen-based wallet has one and a card doesn't. Card users confirm in the app on their phone.
Where is my backup if there are no recovery words?
On the second card of the Dual-Card Set. Both cards hold the same keys, generated inside their secure elements during setup.
What should I do if my card arrives already set up?
Don't use it. A new Cryptnox card always arrives blank. Contact us and we'll help.
Sources
- CoinDesk, 9 October 2026: Ledger investigates potential wallet tampering
- The Verge: Ledger wallet tampering suspected after reports of crypto thefts
Based on Ledger statements of 9–11 October 2026 as reported by the press. Loss estimates come from on-chain investigators and have not been independently verified.