How the Armleder patent family lets bank card schemes move to blockchain
Every card scheme stands on a stack of inventions. The EMV chip, the cryptogram the terminal checks, the way keys are injected in a personalisation bureau, the certificates that prove a card is genuine: each of these was invented, standardised and, in many cases, patented before Visa and Mastercard could run on them. A card scheme that settles on a blockchain needs an equivalent stack, re-thought around one fact that EMV never had to deal with: on a blockchain the key is the account, and a transaction, once confirmed, cannot be reversed.
Over six years, Cryptnox founder Sébastien Armleder has built that stack and protected it. The family today includes four granted United States patents, a granted European unitary patent, a published European application, a granted Chinese patent, and two international patent applications filed in 2026 that are not yet published. The granted and published titles are listed on our patents page. This article explains, in plain language, what each one covers and why together they let a bank, a fintech or any other organisation run a card scheme on blockchain-native infrastructure rather than on a card network.
This article summarises public patent documents for a general audience. It is not legal advice and does not define the scope of any claim.
What a card scheme needs that a wallet does not
A hardware wallet protects one person's key. A card scheme has to do six more things, at scale, for people who will never read a seed phrase.
- Issue hundreds of thousands of cards, by mail, without any party in the logistics chain seeing a secret.
- Authorise every payment against the issuer's rules, even though the issuer must not hold the key.
- Pay at a merchant terminal with a tap, with the merchant and the terminal trusted no more than they are today.
- Recover a lost or damaged card without losing the funds and without a custodian holding everything.
- Govern high-value or corporate accounts with more than one approver.
- Trust the hardware: prove that a card, and the chip inside it, is genuine.
In EMV these functions are delivered by standards, certification programmes and the scheme's own keys. On a blockchain they all have to be rebuilt around a key that lives in a secure element and never leaves it. Published patents in the Armleder family cover issuance, authorisation, recovery, governance and trust.
The family at a glance
| Scheme function | Patent | Status | What it protects |
|---|---|---|---|
| Issue | US 12,132,824 B2, "Method for issuance of a personalized user device" | Granted US (Oct 2024); EP filed; US continuation filed. Priority 22 Feb 2023 | Seedless, remote issuance of a personalised secure device: the card verifies the issuer's signed envelope before decrypting its key material |
| Authorise | US 12,719,697 B2, issuer-controlled co-signing (family of EP 4 258 596 A1, pending, and WO 2023/194161) | Granted US, 25 Aug 2026. Priority 8 Apr 2022 | A card that signs a blockchain transaction only after cardholder authentication and an issuer authorisation element produced after a compliance check |
| Recover | US 11,791,996 B2 and continuation US 12,101,400 B2, "Storing and determining a data element" | Granted US (Oct 2023 and Sep 2024); EP filed. Priority 29 Jan 2020 | Threshold secret sharing where each share is encrypted to a distinct key and the secret is only ever reassembled inside a secure element |
| Govern | EP 4 060 540 B1, secure-element signing device with N-of-M authorisation | Granted European unitary patent, 5 Aug 2026, in force in 18 EU states; US application pending. Priority 17 Mar 2021 | A card that signs only after receiving N copies of a transaction signed by different authorised keys, with encrypted backup cloning and tamper-evident counters |
| Trust | EP 4 148 608 A1 and CN ZL 202211056164.7 | EP published; CN granted | On-card PKI and attestation so that apps, terminals and chains can verify a card is genuine |
| Further filings | Two international (PCT) applications | Filed 2026, not yet published | Not yet public. Details will be published in due course |
with detail pages for each title on the Cryptnox patents page.
Issue: personalised cards without seed phrases (US 12,132,824 B2)
A bank issues cards through a personalisation bureau that injects keys inside a secured facility. A crypto wallet makes the user generate a seed phrase and write it down. Neither model works for mailing a hundred thousand blockchain cards to retail customers.
The issuance patent describes a different path. The chip generates its own key pairs during initialisation and exports only public data and a serial number. The issuer system uses that public data to compute the cardholder's encrypted key material, signs it with the issuer's private key, and sends it back. The card verifies the issuer's signature first, then decrypts with the private key it generated itself. Nothing in between (the bureau, the courier, the phone, the app) ever holds a usable secret.
For a scheme operator this is the personalisation layer. Cards ship ready to activate, with no seed phrase and no branch visit. Because the issuer can re-create the same envelope for a new chip, a replacement card carries the same account, which is how a lost card stops being a lost wallet. On the Cryptnox platform the full activation, including backup card and app pairing, completes in a short sequence of NFC taps.
Authorise: issuer-controlled co-signing (US 12,719,697 B2)
This is the patent that turns a wallet card into a card scheme instrument.
A bank has to enforce rules: spending limits, sanctions screening, allowed recipients, country restrictions, a freeze when a card is reported lost. In a custodial model the bank holds the keys and simply refuses to sign. In a self-custody model the bank has no say at all. Regulators and customers increasingly want neither.
The co-signing patent describes a three-party ceremony between the cardholder's device, the card and the issuer's remote system. The card signs the transaction hash only after two independent gates have passed: the cardholder has authenticated, and the issuer has delivered a signing element, produced after its own compliance check, that the card verifies before it signs. The cardholder's private key stays inside the secure element and never reaches the issuer. The issuer, in turn, cannot produce a valid signature on its own.
In card-scheme terms this is the authorisation host, with one difference that matters on a blockchain: the authorisation is cryptographically bound to the exact transaction and the card refuses to sign without it. A freeze is simply the issuer no longer issuing elements. The patent also describes batch approval, where a single issuer element authorises a set of transactions through a concatenated hash, which is what a corporate payout run or a merchant settlement batch needs.
Granted on 25 August 2026, this patent is the backbone of the C-WaaS authorisation flow described in our article on launching a blockchain card scheme.
Recover: threshold key recovery without a single point of failure (US 11,791,996 B2 and US 12,101,400 B2)
When an EMV card is lost, the bank reissues it from keys in its own vault. When a blockchain key is lost, the funds are gone unless someone else holds a copy, and a single copy held by a single party is exactly the custody risk a scheme operator wants to avoid.
The two "storing and determining a data element" patents cover a method where the secret (a key or a seed) is split into M shares using threshold secret sharing, each share is encrypted individually to a different key, and the encrypted shares are distributed, for example to secure elements in other cards or to separate parties. Reconstruction requires a threshold number of shares, uses temporary keys for transport, and takes place inside a secure element, so the complete secret never exists in cleartext outside certified hardware.
For a scheme this is the recovery and institutional custody layer: backup cards for retail customers, multi-party recovery for private banking clients, and operator-side recovery where no single employee, system or site can reassemble a key alone. It is commercialised today as the Cryptnox Shamir Secret Sharing cards and underpins the recovery options of C-WaaS programmes.
Govern: N-of-M authorisation inside the card (EP 4 060 540 B1)
Corporate cards, treasury wallets and high-value accounts need more than one approver. In software this is a multisig contract; in a card scheme it has to work for any chain, including those with no smart contracts, and it has to survive a compromised phone.
The European patent describes a secure-element signing device that stores M authorised public keys and signs a transaction only after it receives at least N copies of that transaction, each signed by a different authorised key. The authorisation protocol runs inside the chip, so neither the phone nor a server can shortcut it. The same patent also describes PIN-based identification as part of the protocol, key derivation from an on-card seed, an on-card transaction counter that reveals whether a card has ever been used, and a protected procedure for cloning the keys and the authorisation rules to a backup card over an encrypted channel.
Granted as a European unitary patent on 5 August 2026 and in force in eighteen EU member states, with a US application pending, this is the governance layer: four-eyes approval enforced by hardware rather than by policy documents.
Trust: proving a card is genuine (EP 4 148 608 A1 and CN ZL 202211056164.7)
Card schemes run their own certificate authorities so that a terminal can check that a card is real. A blockchain scheme needs the same, and the check has to work for apps, terminals and on-chain services alike.
The European application and the granted Chinese patent cover an on-card public key infrastructure: the secure element holds a certified key and can prove its authenticity to whoever asks, which blocks spoofed cards, cloned apps and impersonation attacks. For a scheme operator this is the trust anchor underneath everything else: the issuer only authorises genuine cards, the terminal only talks to genuine cards, and a chain-side service can verify that a signature came from certified hardware.
How the pieces fit together
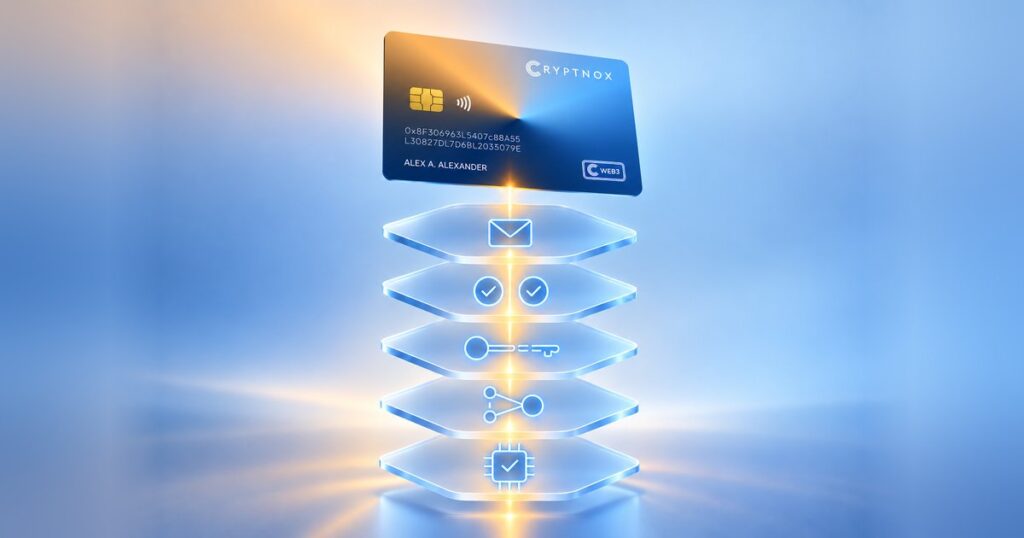
Read top to bottom, the family is a card scheme stack.
| Layer | What happens | Protected by |
|---|---|---|
| Trust | The chip proves it is genuine | EP 4 148 608 A1, CN ZL 202211056164.7 |
| Issue | The card is personalised remotely, no seed phrase, replaceable | US 12,132,824 B2 |
| Authorise | Every payment needs the cardholder and the issuer | US 12,719,697 B2 |
| Govern | Corporate and high-value accounts need N of M approvers | EP 4 060 540 B1 |
| Recover | Keys are backed up as encrypted threshold shares | US 11,791,996 B2, US 12,101,400 B2 |
The point-of-sale layer, where a cardholder taps a card at a merchant terminal and the payment settles on chain, is built on the same authorisation ceremony and has been demonstrated in our development environment. Two further international patent applications were filed in 2026 and are not yet published. We will describe them once they publish.
What this means for a bank
A bank evaluating a card scheme on blockchain rails has three ways to get the technology: build it, buy a custodial white-label product, or deploy a protected, non-custodial stack. Building means re-inventing the six layers above and then defending them. Buying custodial means holding customer keys, with the balance-sheet and regulatory weight that brings. Deploying C-WaaS, Cryptnox's blockchain-native card scheme infrastructure built on the Armleder family, means issuing cards whose keys stay with the customer, under rules the bank enforces, on hardware the bank can certify, with a patent position behind the design.
The migration path is gradual by design. A dual-technology card keeps Mastercard or Visa on the same plastic while the bank's own blockchain scheme grows merchant by merchant. Every layer the bank adds along the way, from issuance to recovery to corporate governance, is already covered.