The Binance hack: why a blockchain-native card scheme has no hot wallet to drain
On 29 October 2026 about USD 6.3 billion left Binance's hot wallets on ten chains in twenty minutes, without a stolen key or a contract bug. Here is what is known, and why a card scheme that settles on chain has no hot wallet to drain.
On the evening of 29 October 2026, between 20:04 and 20:24 UTC, an attacker moved most of about USD 6.3 billion out of Binance's hot wallets on ten blockchains. It is the largest theft in the history of the asset class, roughly four times the Bybit heist of February 2025. Binance paused withdrawals, said it would cover every loss from its insurance fund and its own money, and about USD 3 billion was frozen within hours by Tether, Circle and others.
First, the thing that should be said plainly: Binance's customers appear to be whole, the response was fast, and the adversary assessed by TRM Labs and Chainalysis is a state-backed unit that has beaten some of the best-defended companies in the industry. This is not a story about carelessness.
It is a story about architecture. The attacker did not steal a private key. The attacker did not exploit a smart-contract bug. The attacker found a pool of customer money behind a signing system, reached that system from one engineer's laptop, and the signing system signed what it was asked to sign. That combination, a pool plus a signer that cannot say no, is what every large exchange heist has in common. It is also exactly what C-WaaS (Card Wallet as a Service), our blockchain-native card scheme infrastructure, was built not to have. This post walks through what is known about the Binance attack, and then walks the same attacker through a blockchain card scheme to show where the path ends.
What is known so far
Binance's own statement, posted at 02:25 UTC on 30 October, says the incident "may involve a compromised DevOps engineer's laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions", and that the investigation found "no evidence of any wallet private key leak". Co-CEO Richard Teng added that the attacker "did not simply use one engineer's permissions" and that this "was not a single 'one-click' action". On 31 October Binance added that its investigation had found further points of breach beyond the laptop, without saying where, and the FBI attributed the attack to North Korea's TraderTraitor group.
The independent analyses fill in the shape of it:
- Staging. The operator's wallet was funded through Tornado Cash on 28 October, about 36 hours before. Malicious code was tested on trial wallets before the real run.
- One foothold, ten chains. Between 20:04 and about 20:30 UTC, Binance wallets on Ethereum, Bitcoin, Tron, the XRP Ledger, Solana, Arbitrum, Optimism, Base, Avalanche and Polygon all produced valid signatures for the attacker. Those wallets use different key types and different signature schemes. TRM Labs' reading is that "the attacker gained the ability to make Binance's hot wallet signing system sign transactions of its choosing across chains". Blockaid's CEO called it "key misuse, not key leakage".
- The numbers. About 200,630 ETH and 185 tokens on Ethereum (around USD 3.8 billion, including 1.6 billion USDT from one wallet), 18,270 BTC (around USD 1.5 billion), 612.7 million USDT and 46.4 million TRX on Tron, 233 million XRP, 970,500 SOL, and smaller amounts elsewhere.
- The freezes. Tether froze about 1.77 billion USDT, Circle about 825 million USDC, with Ripple, World Liberty and the Arbitrum Security Council adding more. Roughly USD 2.4 billion in ETH and BTC remains beyond anyone's reach.
The Ethereum trick, in plain words
The part of the attack everyone is quoting happened on Ethereum, and it is worth understanding because it says something about what "no smart contracts" is worth.
Since the Pectra upgrade in May 2025, an ordinary Ethereum account can sign a short authorization that says "let this contract's code act as me". Submitted in a transaction, it turns the account into whatever the contract says it is. Each authorization is only valid at one exact transaction count (the account's nonce). Binance's biggest hot wallet, known as Binance 14, was processing live customer withdrawals, so its nonce was moving every few seconds and the attacker could not know which value would be current at the moment of inclusion.
So the attacker had the signing system sign fifty authorizations, for fifty consecutive nonces, and submitted all of them in a single transaction at 20:20 UTC. One matched. From that moment, Binance 14 ran the attacker's sweeper code. Three and a half minutes later a single call to that code moved 167,464 ETH, 1.6 billion USDT and sixty other tokens, leaving one ETH behind for gas. The delegation stayed in place for almost four hours and was used six more times before Binance revoked it just after midnight.
Nothing in that sequence was a bug. The chain honoured valid signatures. The contract was the attacker's own tool, installed onto the hot wallet using the hot wallet's own signature. The failure was upstream: a signer that would sign fifty delegations to an unverified contract without anything saying no.
Three heists, one architecture
This is the third time Binance's own history, or that of its closest peer, has shown the same shape.
| Heist | Binance, May 2019 | Bybit, February 2025 | Binance, October 2026 |
|---|---|---|---|
| Loss | 7,000 BTC, about USD 41 million | About 401,000 ETH, about USD 1.5 billion | About USD 6.3 billion on ten chains |
| How the attacker got in | Phished API keys and two-factor codes from many user accounts | A wallet vendor's developer laptop, then the vendor's cloud account, then the web page the signers used | A DevOps engineer's laptop, then a service container |
| What was fooled | The withdrawal checks | The three human signers, whose screens showed a harmless transfer while they approved a contract swap | The signing system itself |
| Key stolen? | No | No | No, per Binance |
| Contract bug? | No | No | No |
| Where the money sat | One hot wallet | One multisig wallet | Hot wallets on ten chains |
Different mechanisms every time. The constant is a pool of customer funds behind a signing authority that an ordinary employee endpoint can reach. The pool is what turns an intrusion into a headline: without a wallet holding USD 2.5 billion, fifty signed authorizations are an incident report, not a crisis.
Why exchanges have hot wallets at all
An exchange is a custodian. Your balance is a row in its database; on chain, the funds backing all those rows sit pooled in a handful of addresses so that withdrawals can be served in seconds. The addresses that serve withdrawals are hot by definition: their keys are online and connected to the withdrawal system. Cold storage holds the rest, but the hot pool is still enormous because customers expect instant withdrawals at any hour.
That is why "hot wallet vs cold wallet" is the wrong frame for this incident. Binance has cold storage. The attack took the hot pool, and the hot pool alone was worth more than most exchanges' entire reserves. The question is not how much sits in cold storage. The question is whether there is a pool at all, and whether the thing that signs for it can tell a good instruction from a bad one.
Issuers and processors: see the authorisation path on a live card and terminal. Book a demo of the C-WaaS blockchain card scheme.
How a blockchain-native card scheme is built differently
C-WaaS is blockchain-native card scheme infrastructure: a complete card issuing and payment processing infrastructure with direct on-chain settlement, which a bank, an issuer or a fintech runs as its own card scheme under its own licences. It is not an exchange and it is not a wallet app. It is the same shape as a conventional card scheme, with the chain as the settlement layer. Five properties matter here.
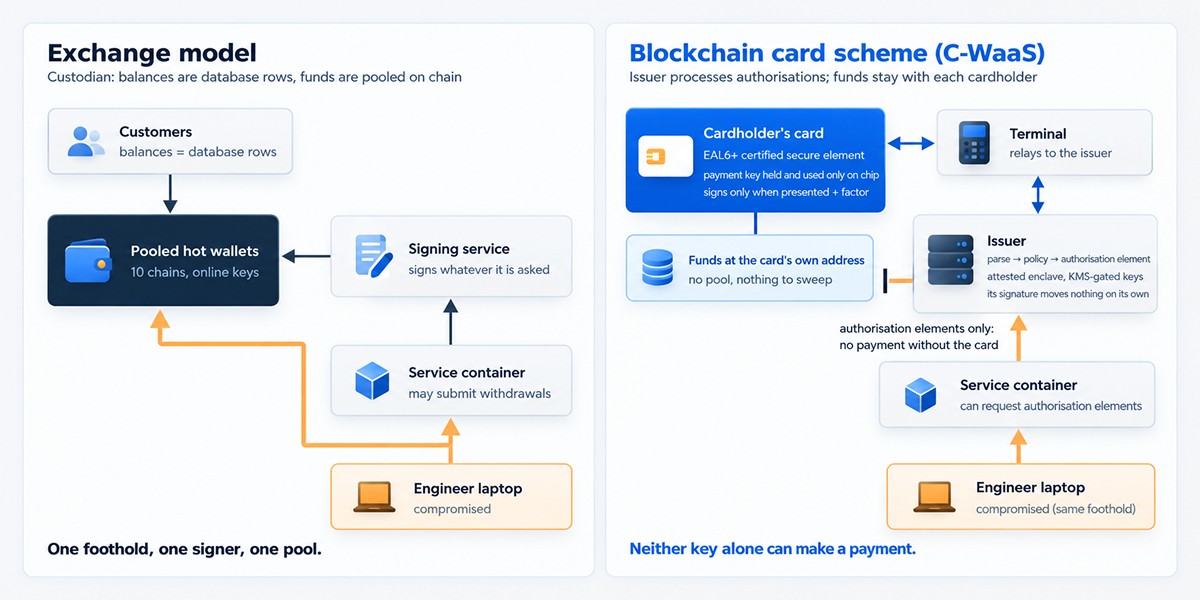
1. There is no pool. Each cardholder's funds sit at the card's own on-chain address. That address belongs to a payment key that is held and used only inside the card's EAL6+ certified secure element: it reaches the card through the patented issuance process (US 12,132,824) and never leaves the chip afterwards. No issuer-side address holds customer funds, so there is no hot wallet to sweep.
2. The issuer never signs a payment. When a card is tapped at a terminal, or used from the cardholder's phone, the issuer receives the transaction, parses it, and checks it against policy: known chain, allow-listed asset, approved payout address, per-transaction and monthly limits, step-up above a threshold. Only then does it produce an authorisation element, a signature by a per-card issuer key that lives in an attested AWS Nitro Enclave with KMS-gated keys. That authorisation element moves no money. The card verifies it, checks the cardholder's factor (the card's PIN, the paired phone, or a POS passcode above the threshold) and only then signs the payment with its own key. Neither key alone can make a payment. (How aggregate control is classified for custody purposes is a question for each issuer's counsel; we do not call this self-custody.)
3. What gets signed is a transaction, not a hash. The issuer rebuilds the transaction from its fields and computes the hash itself; a request whose hash does not match the rebuilt transaction is rejected before anything is signed. Token transfers are decoded against the allow-listed token's interface, and only a plain transfer to an approved address passes. An account delegation of the kind used against Binance 14 is not a transaction the scheme can authorise, because it cannot be expressed through the authorisation interface at all.
4. There are no smart contracts of our own. Cards are ordinary accounts. Settlement is a plain transfer of the native asset or of a stablecoin through the stablecoin issuer's standard transfer function. The scheme deploys no contracts, no upgradeable logic, no delegation, no approvals that could be redirected later. The Bybit attack needed a multisig contract to swap; the Binance attack needed a delegation to install. Neither has anything to attach to here.
5. The issuer can stop a card. Blocking a card stops the issuer's authorisation elements, and a card without them cannot pay anything, anywhere. Stablecoin freezes remain available on top of that, but the scheme does not have to ask anyone's permission to stop its own cards.
Walk the same attacker through a blockchain card scheme
Give the attacker the identical starting point: an engineer's laptop at the issuer, and from it, a container inside the issuer's backend.
Step one, reach the signer. On C-WaaS the issuer's signer produces authorisation elements. Suppose the attacker gets authorisation elements for anything they like. They now hold signatures that move nothing.
Step two, move funds. The chain accepts only the card's signature. A card signs only while it is physically presented or acting through its paired phone, only after it has verified a valid authorisation element, and only after the cardholder's factor is satisfied. The attacker's problem has changed from "sign a transaction" to "get every cardholder to tap their card for me, within limits, to an approved payout address".
Step three, scale. At Binance the blast radius was every hot wallet on ten chains in twenty minutes. Here it is bounded by the cards actually in use at that moment, one transaction each, within per-transaction caps, to allow-listed destinations, with the issuer able to block cards as soon as monitoring fires. There is no wallet to delegate, no batch to sweep, no cross-chain signing authority to hijack.
Step four, exit. Approved payout addresses belong to registered merchants. They are known to the issuer and reachable by law enforcement. The fifty-authorization trick, the nineteen-way Bitcoin split and the sprint out of stablecoins before the freezes all depend on an attacker controlling the destination. On a card scheme, the destination was approved before the signature existed.
Would something similar have happened on C-WaaS? Not the thing that happened. The same intrusion yields, at worst, a bounded number of in-limit, in-allow-list payments from cards in use at that moment, which the issuer can stop. The USD 6.3 billion outcome requires a pooled balance under an operator key and a signer whose signature is the payment. The scheme has neither.
What this does not protect against
Honesty is part of security, so here is the other side.
- A cardholder who loses a card together with the PIN or the paired phone can lose what the limits allow before the card is blocked. Limits bound it; they do not prevent it.
- Stablecoin issuers can freeze any address, including a cardholder's, and chain-level events are outside anyone's scheme.
- If the issuer's authorisation service is down, no card can pay. That is the safe direction to fail, but it is still an outage, and it is why the authorisation path is built for availability as much as for security.
- Issuance, the process that provisions a card's payment key, is the most sensitive operation in the scheme. It runs inside attested enclaves under split administrative control and is not reachable from the payment path; it is where an issuer's strongest access controls belong, and where ours are concentrated.
- No system is unhackable. The claim here is narrower and, we think, more useful: the scheme has no component whose compromise drains everyone.
What we take from it for ourselves
The Binance incident is a reminder that the signing path, not the key store, is where modern attacks land. We treat it that way: policy runs before any signature; authorisation keys live in attested enclaves and never in an engineer's reach; production access is separated by account and role with no standing credentials; and every cardholder's balance is reconciled against the chain so that any movement the issuer did not authorise is caught, not discovered weeks later. Those are operating disciplines, and they are the same ones every exchange is now re-examining. The difference is what they protect: on an exchange, a pool; on a blockchain card scheme, an authorisation.
Sources
- Binance statement on X, 02:25 UTC 30 October 2026, as reported by BleepingComputer and FinanceFeeds; Richard Teng quote via DisruptionBanking.
- Binance update (further points of breach, about USD 3 billion frozen) and FBI attribution, 31 October 2026: ABC News.
- TRM Labs, North Korea Steals USD 6.36 Billion From Binance.
- Bitquery, Binance Hack on-chain investigation.
- Blockaid via Cointelegraph; EIP-7702 detail via crypto.news and Valletta Software.
- Bybit, February 2025: Sygnia investigation.
- Binance, May 2019: TechCrunch.
Facts as of 2 November 2026. Statements about Binance are Binance's own or those of the named analysts, dated; attribution of the attack is as assessed by TRM Labs and Chainalysis and, since 31 October, by the FBI.