Card-not-present fraud: the biggest fraud category in card payments, and why it cannot exist on a C-WaaS card scheme
Every year the card industry publishes its fraud figures, and every year the same category dominates: card-not-present. Payments where the card is not physically read, which means almost all online payments, account for the large majority of fraud losses on cards in Europe and in the United States. The industry has spent two decades building defences around that fact: 3D Secure, strong customer authentication, tokenisation, machine-learning risk engines, and a chargeback system to clean up afterwards.
This article explains why card-not-present fraud exists at all, what it costs, and why a card scheme running on C-WaaS, Cryptnox's blockchain-native card scheme infrastructure, does not have the category. Not "reduces it". Does not have it, for a structural reason: there is no static credential on a C-WaaS card that a fraudster could take and reuse.
The numbers
- Payment card fraud losses worldwide were USD 33.41 billion in 2024, according to the Nilson Report (January 2026). The Nilson Report projects USD 41.06 billion by 2030.
- The United States accounted for 26.31 percent of global card volume in 2024 but 41.87 percent of global fraud losses, which Nilson attributes to the US being the top region for online purchases, "which are more susceptible to fraud".
- In the European Economic Area, total payment fraud reached EUR 4.2 billion in 2024, up from EUR 3.5 billion in 2023. Fraud losses on card payments with cards issued in the EU/EEA were EUR 1.329 billion, up 29 percent year on year (EBA-ECB 2025 Report on Payment Fraud, December 2025).
- The same report finds that around 83 percent of card fraud value came from remote card payments, even though most card transactions happen at a physical point of sale, and that card fraud was 17 times higher when the payee was outside the EEA, where strong customer authentication is not legally required.
Why card-not-present fraud exists
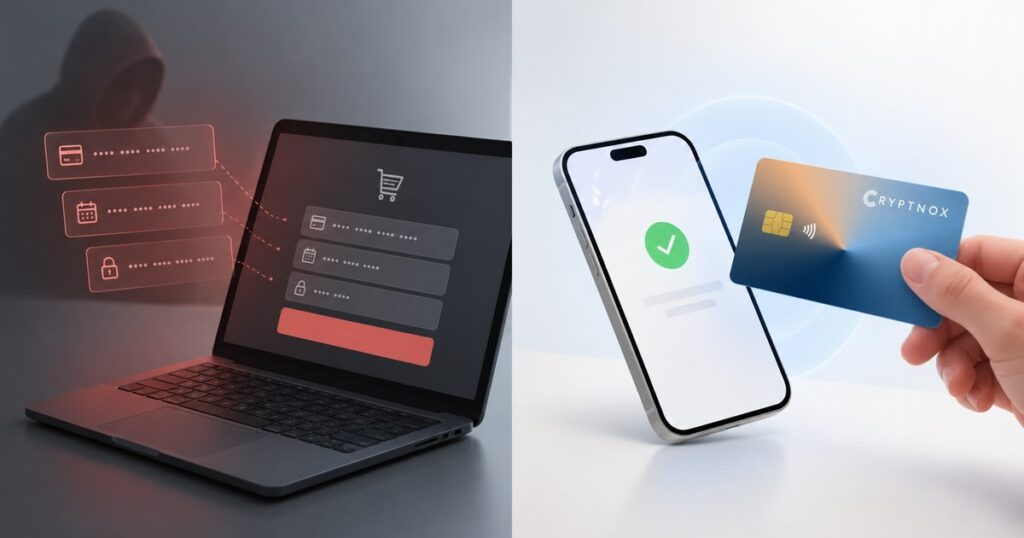
A legacy card scheme authorises payments with a credential: the card number, the expiry date and the three-digit security code. Whoever presents those values can pull money from the account. The credential is static (it is the same for every purchase for years), it is widely shared (every merchant, gateway and processor in the chain sees it), and it is replayable (presenting it once is indistinguishable from presenting it again).
That combination is the whole story of card-not-present fraud:
- Capture. Card data leaks from merchant databases, phishing pages, skimmed web forms, infected devices and insider theft. Because the data is shared with every merchant, the attack surface is the entire internet.
- Reuse. The stolen credential works at any merchant that does not insist on a second factor, in any country. The EBA-ECB finding that fraud is seventeen times higher outside the EEA is the direct consequence: wherever strong customer authentication is not applied, the static credential is enough.
- Clean-up. The scheme's remedy is the chargeback: the cardholder disputes, the issuer reverses, the merchant pays. Chargebacks cost merchants the goods, the fee and sometimes their account, and they created a fraud category of their own, "friendly fraud", where legitimate purchases are disputed.
The defences the industry built are all attempts to add something dynamic on top of the static credential. 3D Secure asks the issuer to authenticate the cardholder in the browser. Network tokenisation replaces the card number with a merchant-specific token. Strong customer authentication, under European law, requires two factors for most online payments. They work, measurably. They are also optional at the edges, uneven across borders, and bolted on to a model whose core assumption, that knowing the number is proof of the right to pay, remains false.
What the chip did right, and why it stopped at the counter
Card-present fraud was solved once before. The EMV chip replaced the magnetic stripe's static data with a cryptogram the chip computes for each transaction, using a key that never leaves it. Counterfeit-card fraud collapsed in every market that migrated. The lesson was clear: a payment should be authorised by a fresh signature from tamper-resistant hardware, not by a reusable secret.
The lesson never reached the online channel, because the chip was only present at the physical terminal. Everywhere else the card number kept doing the work, and fraud moved there. Card-not-present fraud is what happens when a scheme has a dynamic security model for one channel and a static one for the other.
Read how the card scheme works or visit the C-WaaS page.
Why C-WaaS does not have the category
A C-WaaS card scheme has no card-not-present channel because it has no card credential.
This applies to payments made with the C-WaaS wallet application. On a dual-tech or triple-tech card, the EMV application keeps a conventional card number and stays under the rules and fraud protections of its own card scheme. Everything below describes C-WaaS payments.
There is no number to steal. A C-WaaS card has no primary account number, no expiry date and no security code that authorises anything. What is public about the account is a blockchain address, and an address can only receive. Knowing it gives a fraudster the ability to send the cardholder money, nothing more.
Every payment is a fresh signature from the card. To move funds, the transaction must be signed by the key inside the card's EAL6+ certified secure element, and that key never leaves the chip. The signature covers the exact transaction (amount, asset, destination) and nothing else, so it cannot be reused for a different payment. This is the EMV cryptogram's logic applied to every channel, with the chip itself producing the signature.
The issuer must also authorise. The card will not sign unless the issuer has approved the specific transaction and returned an authorisation element the card verifies first, a mechanism protected by US patent 12,719,697 B2. A fraudster therefore needs the physical card, the cardholder's factor and the issuer's approval of that exact payment. There is no single secret that substitutes for all three.
Merchants and terminals receive nothing reusable. At the point of sale the terminal relays an authorisation only the card can use, and it never holds a cardholder key. Online, the cardholder pays by tapping the card on their own phone inside the app, or through WalletConnect: the card signs, exactly as it does at a counter. In C-WaaS terms every payment is card-present, including the ones made from a sofa. A merchant database breach yields public addresses and transaction references, none of which authorises a payment.
Replay and cloning are closed by design. Each card signature is bound to a fresh challenge and to the specific transaction, so an intercepted exchange cannot be replayed. The card's key cannot be extracted, so the card cannot be cloned. Lost or stolen cards are frozen by the issuer refusing further authorisations, and payments above a threshold need a second factor from the cardholder in any case.
What fraud remains, and how a scheme deals with it
Removing card-not-present fraud does not remove fraud. It removes the category that lives on stolen credentials, which is most of the loss, and leaves the categories that live on people.
- Social engineering and authorised push payment fraud. A cardholder persuaded to pay a fraudster will still tap. The scheme's defences are the issuer's rules: spending limits, allowed recipients, step-up confirmation above a threshold, and the operator's policies for new payees. These are enforced before the card signs, not reversed afterwards.
- Merchant non-delivery. Without network chargebacks, consumer protection becomes a scheme rule the operator writes: merchant guarantees, dispute handling, or holding arrangements for specific merchant categories. This is a design decision for the scheme, and a deliberate one, because reversibility is exactly what fed friendly fraud.
- Account takeover. Taking over the cardholder's app does not yield a signature; the card must still be tapped. Taking the card does not yield one either, without the cardholder's factor and the issuer's approval.
In short, the fraud that remains is the fraud that exists in every payment system, including cash and bank transfers, and the scheme has tools to bound it. The fraud that disappears is the one that only exists because legacy schemes authorise payments with a reusable secret.
What this means for an issuer
For a bank or fintech running a card programme, card-not-present fraud is a loss line, an operations team, a 3D Secure contract, a tokenisation project and a PCI DSS scope. On a C-WaaS card scheme there is no card data to protect, no network chargeback queue to staff, and strong authentication is not a regulation to comply with but the only way a payment can happen. The issuer's fraud work moves from detecting misuse of credentials to setting the rules the card enforces. That is a smaller problem, and a more honest one.
See C-WaaS, read about the patents behind it, or contact us.